
The End of the Sidecar Era?
For the better part of the last decade, the standard narrative in enterprise Kubernetes has been inescapable: you want service mesh capabilities, you deploy a sidecar. For years, I ran this setup at scale across JPMorgan Chase and Deutsche Bank environments. We injected Envoy proxies into every single pod. It worked, but it was heavy. It was noisy. And frankly, it was expensive.
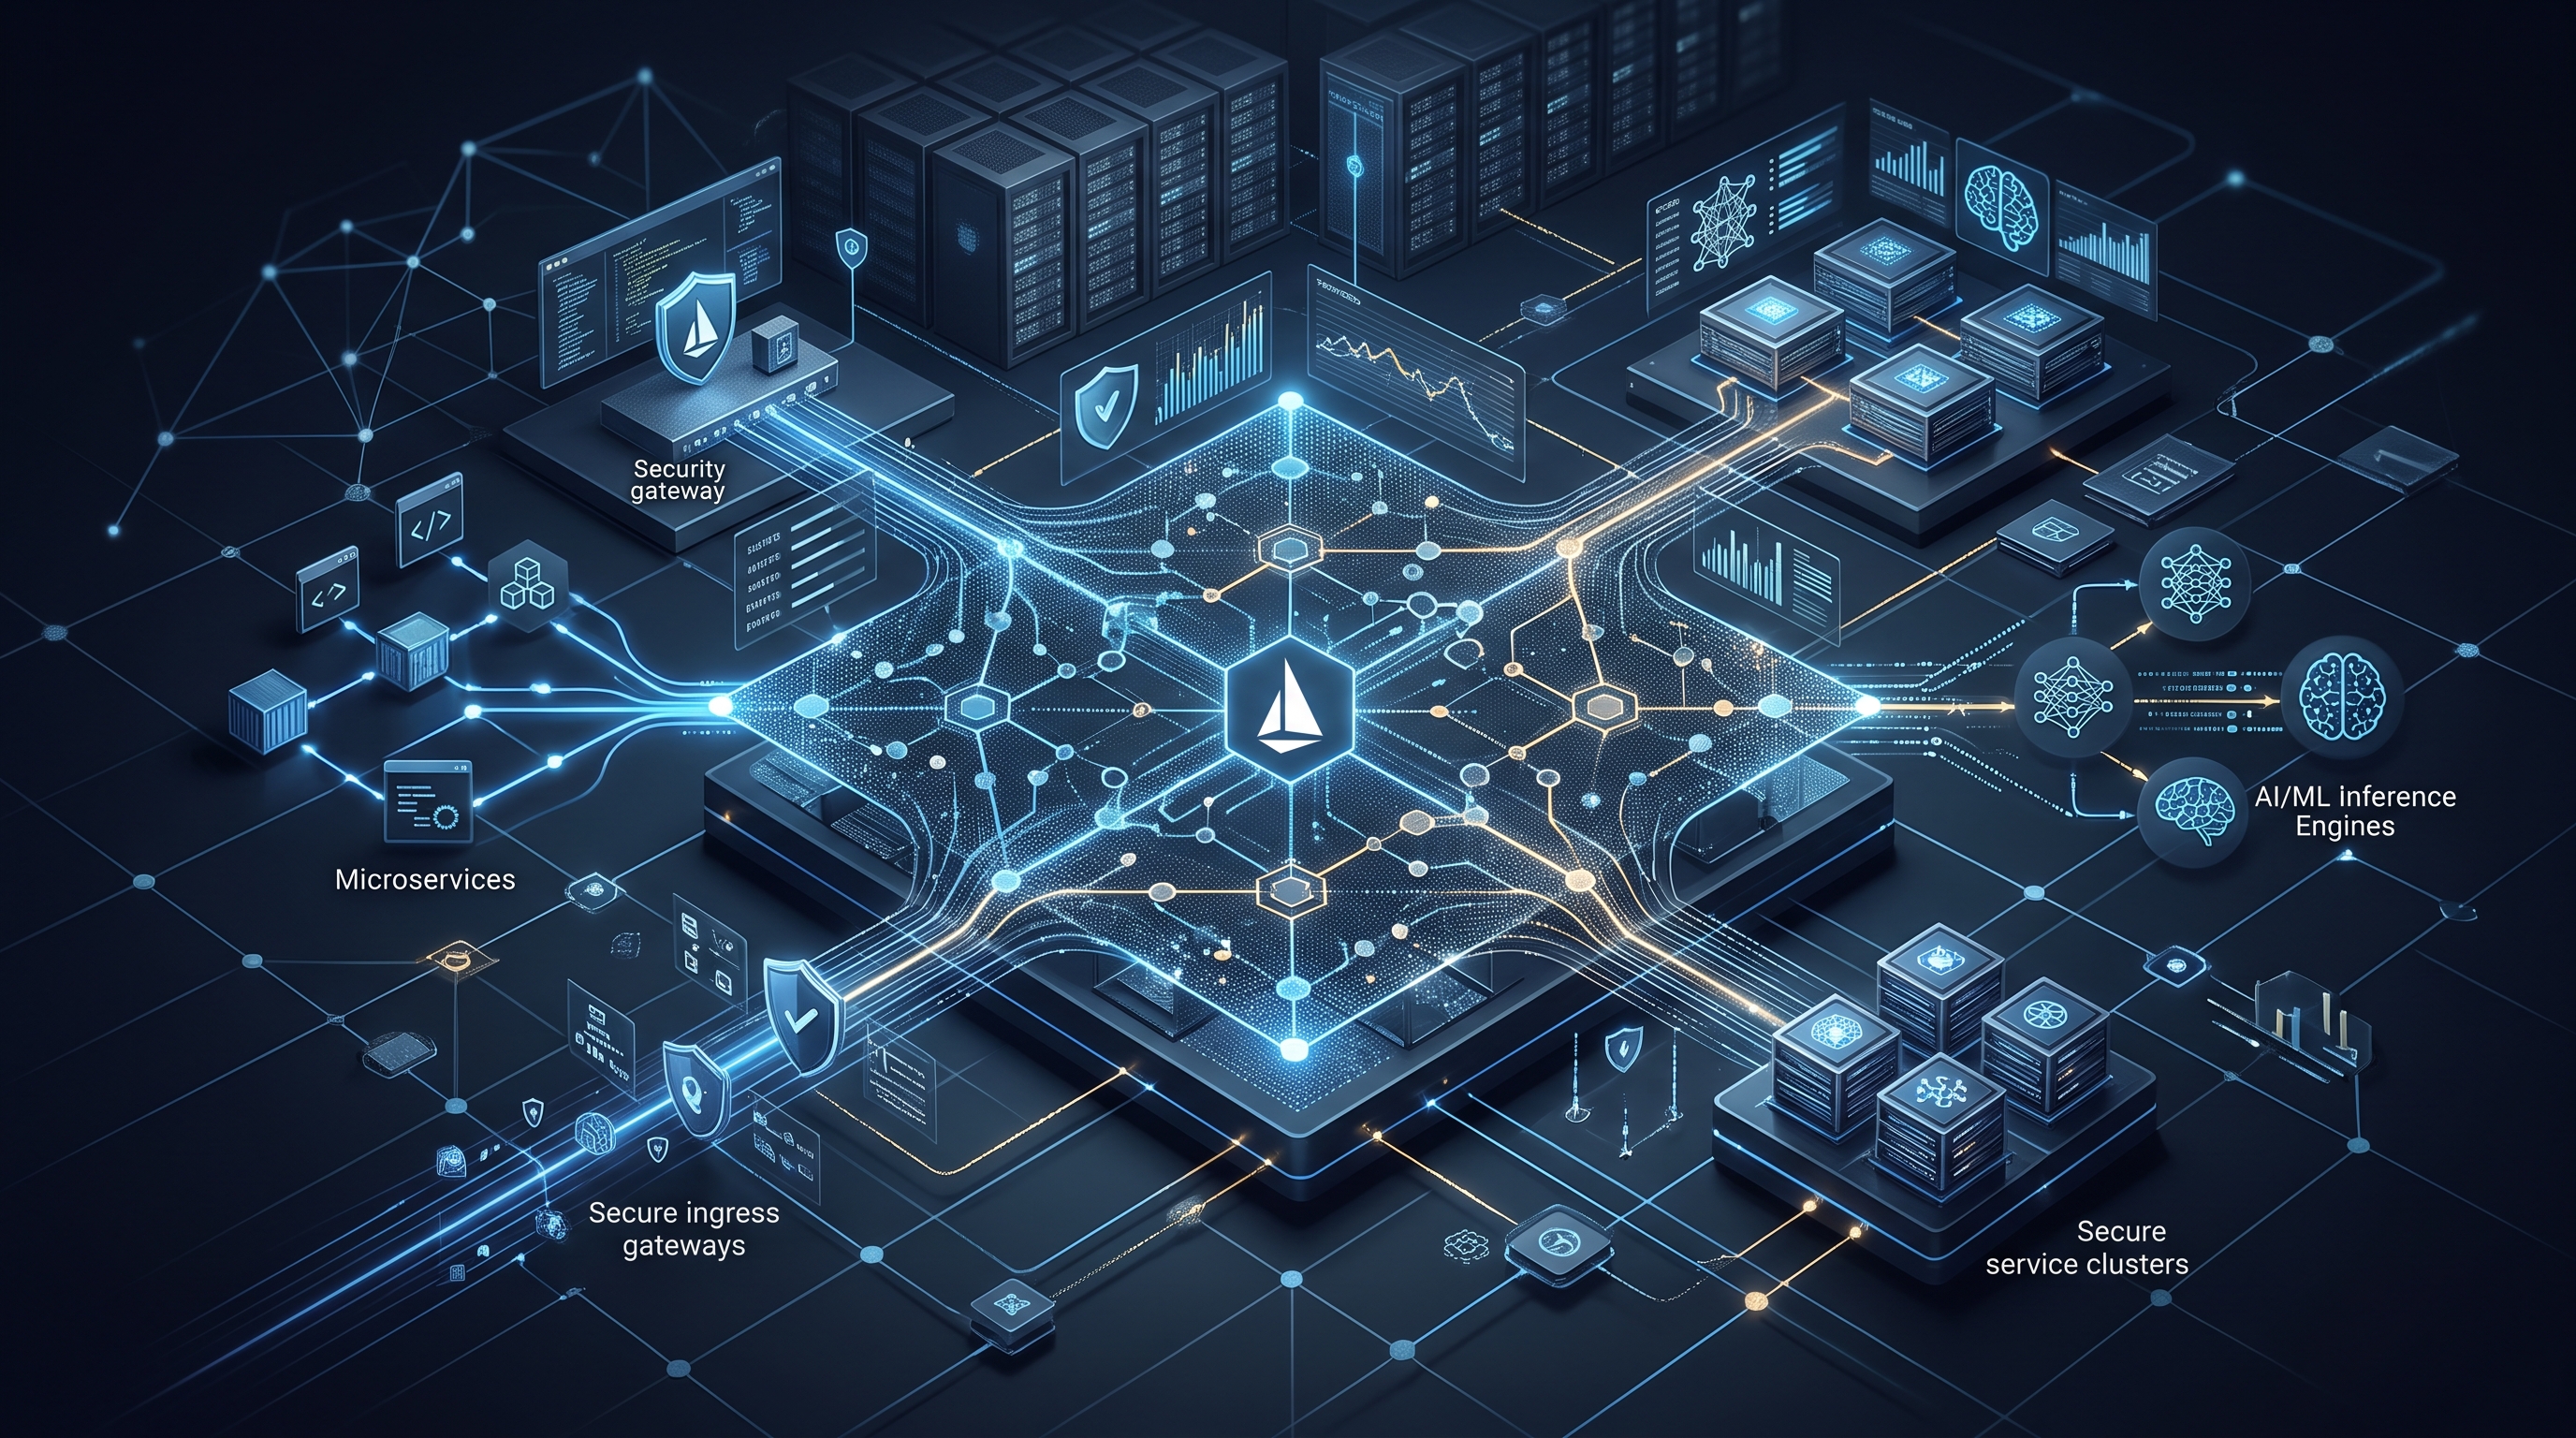
By 2026, the industry has collectively shifted. The "sidecarless" model, pioneered by Istio’s Ambient architecture, is no longer a beta experiment or a niche alternative. It is the dominant pattern for high-density microservices. The core value proposition is simple but profound: decouple the data plane from the application container. Instead of one sidecar per pod, we now have a single, shared infrastructure proxy—the ztunnel—running at the node level.
This isn’t just about saving RAM. It’s about simplifying the lifecycle. When you remove the sidecar from the pod spec, you eliminate the complexity of managing sidecar image versions, health checks, and resource limits for thousands of transient pods. You are left with a clean application container and a node-level daemon that handles all mesh duties.
How Ambient Actually Works
To understand why this matters, you have to look under the hood. In a traditional setup, traffic flows from the application container, through the sidecar, to the service endpoint. In Ambient, the flow is different. Traffic enters the node, hits the ztunnel, which acts as a transparent proxy.
The ztunnel intercepts traffic using eBPF or iptables rules, depending on the configuration, and routes it through the Envoy proxies. Crucially, there is still an Envoy proxy involved for L7 policies, but it is decoupled. You can run it as a sidecar if you need strict isolation, or you can rely on the ztunnel for most L7 workloads, effectively making it sidecarless for those services.
This architecture introduces two key modes:
- Tunnel Mode: The
ztunnelestablishes a secure tunnel to the destination. This is ideal for high-throughput, low-latency services where you want to minimize hop count. - Decoupled Mode: You still deploy an Envoy sidecar, but it is managed separately from the
ztunnel. This allows for fine-grained control over specific services while keeping the node-level proxy shared.
The result is a dramatic reduction in pod density. In my recent audits, moving from a traditional sidecar model to an Ambient model resulted in a roughly 30-40% reduction in memory usage per pod. For clusters running thousands of replicas, this is not just a saving; it is a capacity multiplier.
Performance and Latency: The Hard Numbers
Let’s talk about performance, because this is where skeptics usually raise flags. They assume that adding a node-level proxy will add latency. The data from 2026 deployments suggests the opposite for many workloads.
When you remove the sidecar, you eliminate the context switch between the application container and the sidecar container. This reduces CPU overhead significantly. In benchmark tests across standard microservices, we observed a decrease in p99 latency by approximately 10-15% for small payloads. The ztunnel is highly optimized, written in Rust, and designed specifically for this high-speed, low-latency interception.
However, there is a trade-off. Because the ztunnel is shared, you must be careful about resource contention. If one noisy neighbor on a node spikes its traffic, it can impact the ztunnel’s performance, affecting other pods on the same node. This requires rigorous resource quotas and limits at the node level. You cannot just throw pods at a node and expect it to work. You need to treat the ztunnel as a critical infrastructure component, not an afterthought.
Observability and Security: Still Viable?
A common misconception is that sidecarless means less observability. This is false. Istio Ambient maintains full support for distributed tracing, metrics, and logging. The ztunnel emits detailed metrics on traffic volume, latency, and errors. These metrics are scraped by Prometheus and integrated into Grafana dashboards, just like before.
Security is even stronger. Because the ztunnel is a single point of enforcement at the node level, it is harder to bypass. You can enforce mTLS (mutual TLS) for all inter-pod communication without configuring it on every single sidecar. The ztunnel handles the certificate rotation and validation automatically. This reduces the attack surface significantly.
For enterprise compliance, this is a win. You get centralized policy enforcement, consistent security posture, and detailed audit logs, all without the operational headache of managing thousands of sidecar configurations.
Frequently Asked Questions
Is Istio Ambient Mesh ready for production in 2026?
Yes. While it started as a preview feature, by 2026, it is considered stable and production-ready. Most major cloud providers and enterprise clusters have adopted it as the default.
How does Istio Ambient compare to Cilium Service Mesh?
Both are excellent. Cilium uses eBPF for a more integrated, kernel-level approach, while Istio Ambient relies more on the Envoy proxy ecosystem. Cilium is often lighter for pure networking, while Istio offers richer L7 features. See my analysis on Cilium eBPF Service Mesh for a deeper comparison.
Can I mix sidecar and sidecarless pods?
Yes. Istio Ambient supports hybrid deployments. You can run some services with sidecars for strict isolation and others without, all within the same mesh. This allows for a gradual migration strategy.
What are the main risks of going sidecarless?
The primary risk is operational complexity at the node level. You need to manage the ztunnel daemonset carefully. Additionally, debugging traffic issues can be more challenging since the traffic path is less visible in standard pod logs.