
The Shift from Toggle to Strategy
After twenty-five years in enterprise banking infrastructure, I’ve watched the industry oscillate between extreme caution and reckless speed. In the early 2010s, we treated deployment as a binary event: code went live, or it didn’t. Today, that model is obsolete. The modern enterprise, particularly those running complex Agentic AI deployments, requires a nuanced approach to risk management. This is where feature flags transition from a developer convenience to a core feature flags deployment strategy 2026.
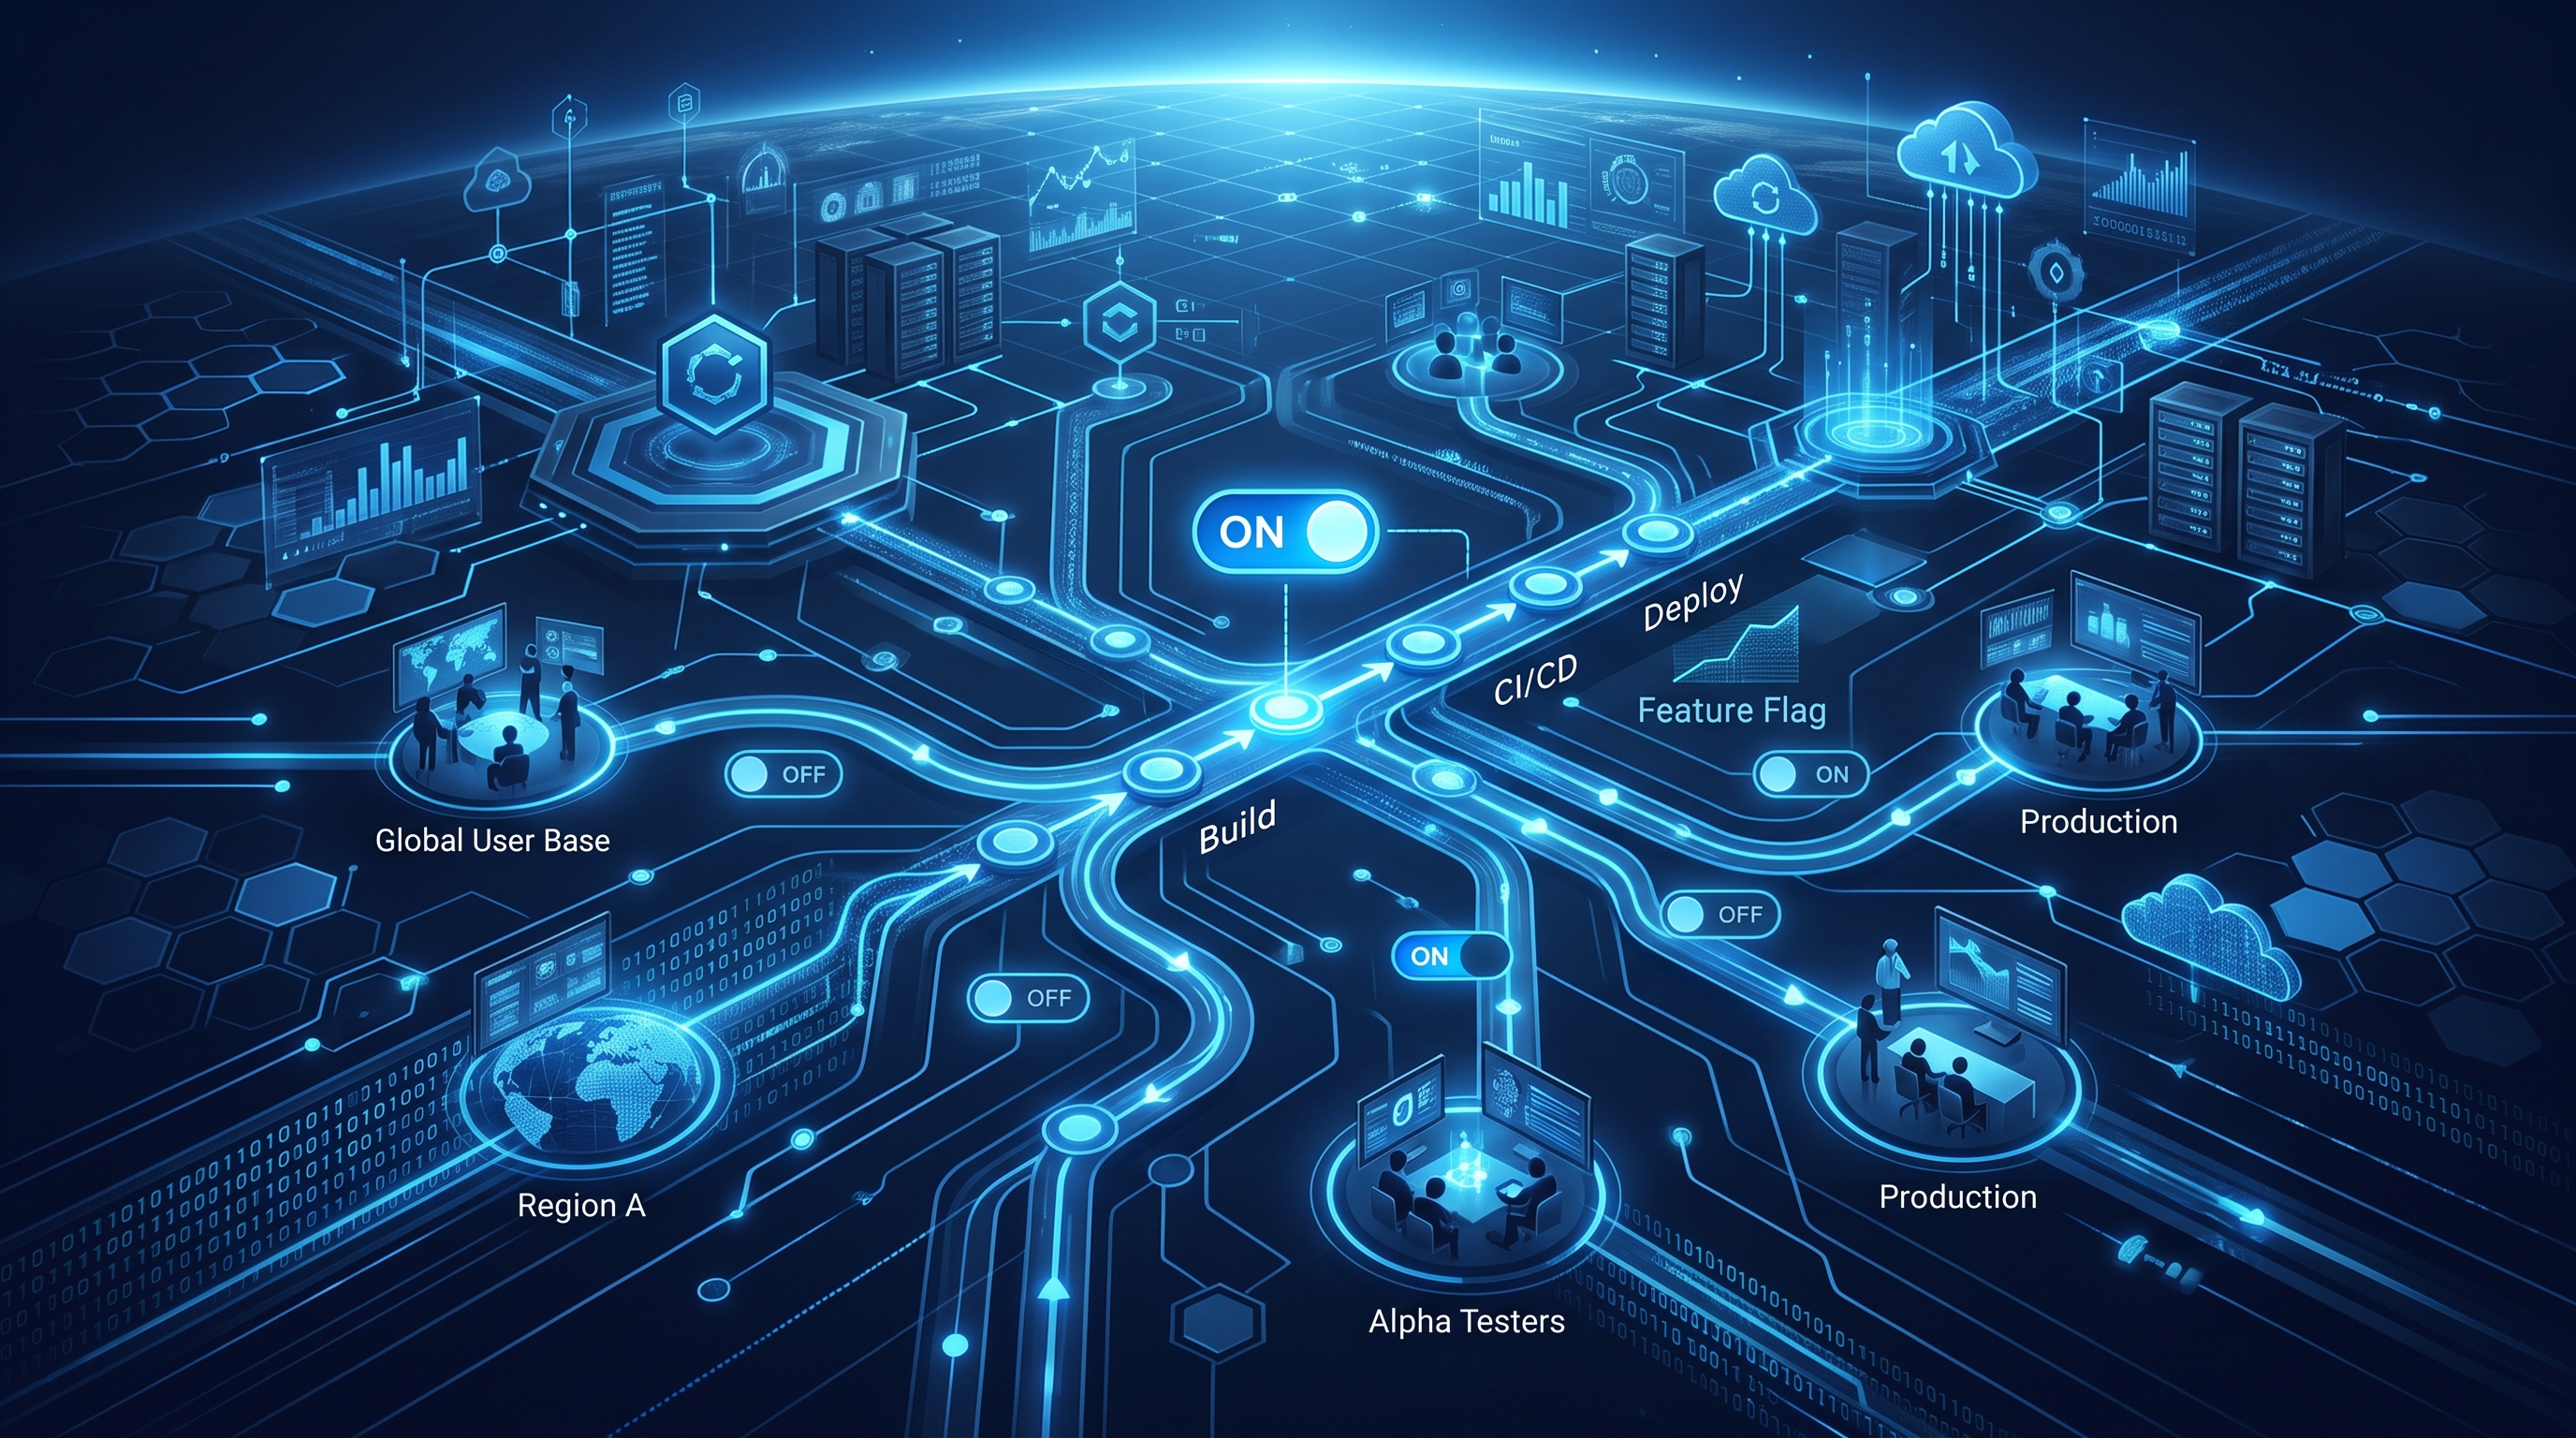
Most organizations still treat feature flags as simple on/off switches for UI elements. This is a fundamental error. A deployment strategy implies governance, rollback capabilities, and controlled exposure. When you view flags through this lens, they become the primary mechanism for decoupling the act of deploying code from the act of releasing features to users. This decoupling is what allows us to maintain high deployment frequencies while keeping the blast radius of any single change minimal.
Decoupling Deployment from Release
The core value proposition of a robust flagging strategy is the ability to merge code into the main branch without exposing the feature to production traffic. In my experience at JPMorgan Chase and Deutsche Bank, we found that this separation allows engineering teams to commit code daily without the fear of breaking production workflows. The code is there, it is tested, and it is deployed, but it remains inert until explicitly activated.
This approach significantly reduces the complexity of release management. Instead of coordinating a multi-team "big bang" release, you can deploy the underlying infrastructure and services continuously. The release itself becomes a configuration change. This is particularly critical when managing RAG systems in Kubernetes, where the interplay between model serving, vector databases, and application logic can be fragile. By keeping the RAG pipeline deployed but the feature flag disabled, you can validate the infrastructure without risking user-facing hallucinations or latency spikes.
- Code is Deployed: The binary is in production, ready to execute.
- Feature is Hidden: The flag prevents the code path from executing for end-users.
- Release is Controlled: Activation is a configuration update, not a new deployment.
Risk Mitigation and Automated Rollback
Speed is useless if it comes with instability. A well-implemented feature flag strategy acts as a circuit breaker. If a new AI agent exhibits unexpected behavior, you can disable the flag in seconds, effectively reverting the feature to its previous state without needing to roll back the entire deployment. This is orders of magnitude faster than a traditional blue-green versus canary deployment rollback, which often requires redeploying containers and waiting for DNS propagation.
I have seen enterprises reduce their mean time to recovery (MTTR) by 40% simply by implementing automated flag-based rollbacks. When a monitoring alert triggers, the system can automatically flip the flag to "off" or "off" for a specific segment, neutralizing the issue before it impacts the majority of users. This is not just about code; it is about operational resilience. In a high-frequency trading environment or a critical banking transaction system, this level of control is non-negotiable.
The Agentic AI Context
The rise of agentic AI introduces new layers of complexity. Unlike deterministic code, AI agents can exhibit non-deterministic behavior. When you deploy an FastAPI-based AI agent, you are not just deploying a function; you are deploying a probability distribution. Feature flags allow you to control the exposure of these probabilistic outcomes. You can limit the flag to a small percentage of users, ensuring that if the agent makes a costly error, the financial impact is contained.
Furthermore, flags allow for dynamic configuration of AI parameters. You can toggle between different model versions, adjust temperature settings, or switch between different retrieval strategies based on user context. This turns the deployment pipeline into a dynamic control plane for AI behavior, rather than a static delivery mechanism for code.
Avoiding the Graveyard
The biggest risk in any feature flag strategy is technical debt. Flags that are never removed create a "flag graveyard," where code paths are hidden but still present, making the codebase harder to understand and test. To avoid this, every flag must have an expiration date and an owner. In my practice, we enforce a rule: flags must be removed within 30 days of general availability. If a flag persists beyond that, it triggers a mandatory refactoring ticket.
This discipline ensures that the deployment strategy remains clean and maintainable. It prevents the accumulation of dead code and ensures that the feature flag infrastructure itself does not become a bottleneck. A clean flagging system is a scalable one. It allows teams to move fast without breaking things, which is the ultimate goal of any modern DevOps organization.
Implementation Essentials
To build a resilient strategy, you need more than just a library. You need a governance model. This includes defining who can create flags, how they are named, and how they are tested. Integration with your CI/CD pipeline is crucial. Tests should verify not just the code, but the flag logic itself. Ensure that flags are evaluated consistently across all environments, from development to production. This consistency is what allows you to trust the deployment process.
- Define Flag Ownership: Every flag must have a clear owner responsible for its lifecycle.
- Set Expiration Policies: Automate the removal of flags that have been active for too long.
- Integrate with CI/CD: Ensure flag changes are tested and versioned like any other code change.
- Monitor Flag Usage: Track which flags are being used and which are ignored to identify technical debt.
Frequently Asked Questions
How do feature flags impact CI/CD pipeline speed?
When implemented correctly, feature flags can increase deployment frequency by 50% or more. By decoupling deployment from release, teams can merge code into the main branch more frequently without waiting for a coordinated release window. This reduces the risk of large, complex merges and allows for continuous integration practices to be fully realized.
What is the difference between a feature flag and a configuration change?
A configuration change typically alters how an application behaves based on environment variables or settings files. A feature flag is a specific type of configuration change that controls the execution of code paths. The key difference is intent and governance. Feature flags are explicitly designed for release management and risk mitigation, often with built-in expiration and ownership tracking, whereas configuration changes are more general-purpose.
Can feature flags be used for A/B testing?
Yes, feature flags are the foundation of A/B testing. By targeting flags to specific user segments, you can expose different versions of a feature to different groups. This allows for controlled experiments where you can measure the impact of a new feature on key metrics before a full rollout. This is particularly useful in AI deployments, where you can test different model versions against each other.